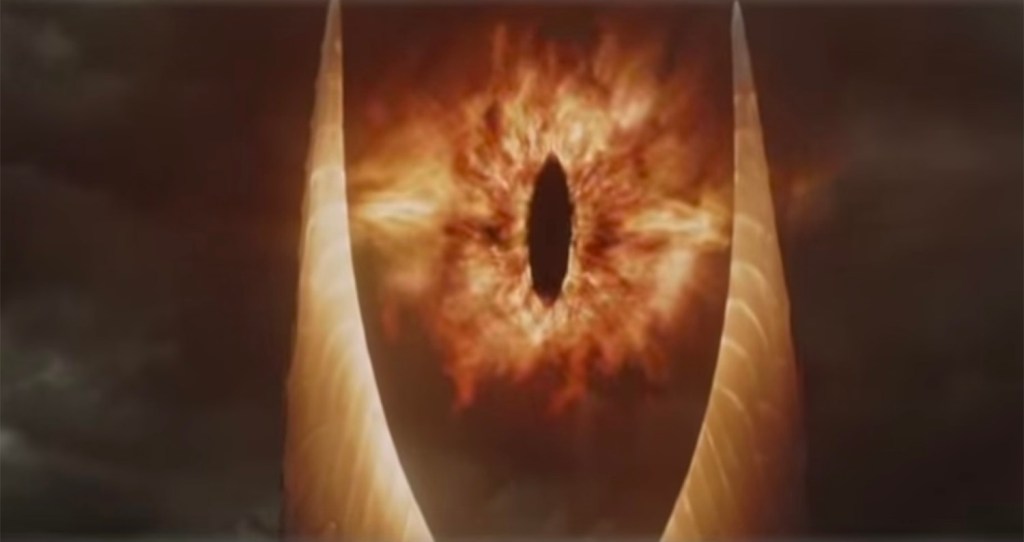
Hackers who appear to have an affinity for the “Lord of the Rings” books have been targeting the governments of Russia, China, Sweden and Belgium for at least five years with the aim of collecting state intelligence, according to researchers at cybersecurity firm Symantec.
The group, dubbed “Strider,” has been using a piece of malware called “Remsec” to conduct its attacks, Symantec said in a report over the weekend. “Remsec is a stealthy tool that appears to be primarily designed for spying purposes,” authors of the report said. “Its code contains a reference to Sauron, the all-seeing antagonist in Lord of the Rings.”
Recommended Stories
Print subscriber? Click here to login/register your account
Digital subscriber? Click here to login/register your account.