
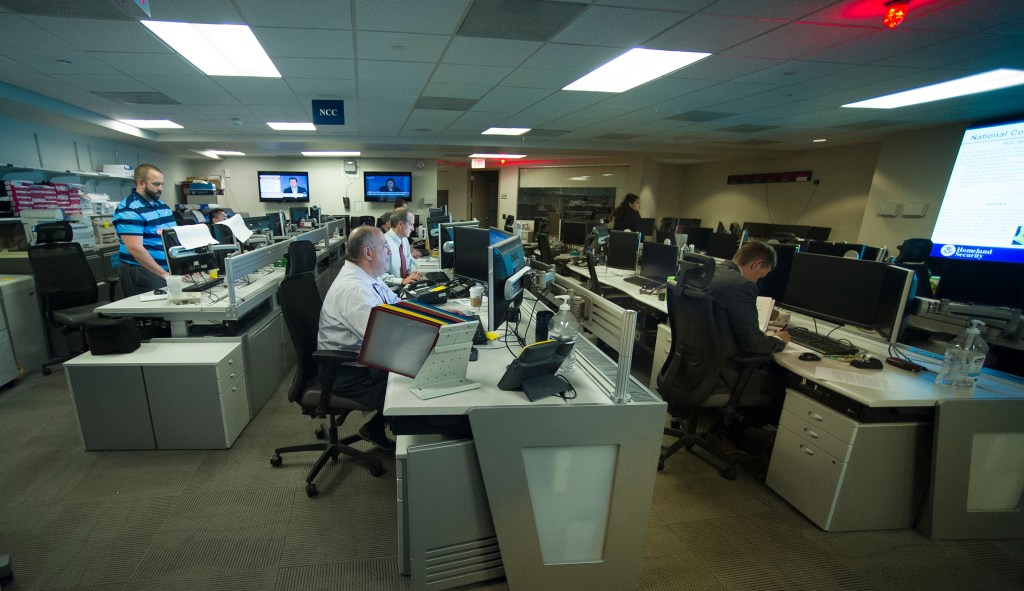
After multiple government data security scandals, the Department Homeland Security gave civil federal agencies one year to bolster email security with a Binding Operational Directive. On Tuesday, that deadline arrived, but many of those agencies that were supposed to be more secure are not. That leaves agencies vulnerable to email fraud and less able to detect malicious senders.
It’s great that DHS set a mandate, but now it must hold agencies accountable for failing to carry it out.
Recommended Stories
Print subscriber? Click here to login/register your account
Digital subscriber? Click here to login/register your account.